Implement once. Evidence many times.
A measure is maintained once and assigned to all requirements it covers. An additional client becomes an additional framework.
ARTURON grc
We develop.Compliance.
Governance · Risk · Compliance
Information security, compliance, audit and business continuity in one management system. One measure base for all frameworks. One tenant per customer.
ARTURON grc is modular software for governance, risk management, information security, compliance, audit and business continuity. It links requirements from frameworks such as ISO/IEC 27001 and NIS-2 with responsible owners, measures and evidence.
An obligation becomes a reliable process
No separate spreadsheet per standard, no new list per client. ARTURON grc links requirements with shared measures and the matching evidence.
A measure is maintained once and assigned to all requirements it covers. An additional client becomes an additional framework.
The assistant considers role, sector, size and group structure. The derivation is stored and recalculated when anything changes.
Keep deadlines in view, compile evidence packages with review and release documents selectively through the Trust Center.
The verifiable link
ISO/IEC 27001, NIS-2 and your client's security annex can require the same measure. ARTURON grc maps these links.
Example: an approved test report documents the recovery test for several requirements. The assignment fits your tenant.
The management system
Seven interconnected areas. Open the modules for a look at the features.
The governance module of ARTURON grc structures policies, organization, objectives and responsibilities in the management system.
Policies with approval, organization, objectives and key figures, values register, PESTEL, SWOT, training and applicability assistant. The management system folgt der harmonisierten Struktur der ISO-Normen.
The risk management of ARTURON grc brings enterprise risks and opportunities together with assessments and measures.
Enterprise risks and opportunities, financial risks and scenarios in bow-tie view. Risks are managed together with responsibilities and measures.
The information security module of ARTURON grc connects risks, assets, protection requirements, measures and evidence in one ISMS.
Risk register with gross and net assessment and approval workflow. Assets and asset groups, protection requirement inheritance, maturity levels, statement of applicability, vulnerabilities, incidents and suppliers. OT security with zones and conduits per IEC 62443.
The compliance module of ARTURON grc assigns requirements to their measures and makes fulfillment status and gaps visible.
Fulfillment matrix with gap analysis and reporting. Product management with SBOM and conformity evidence for the Cyber Resilience Act. Data protection with record of processing activities, impact assessment and data subject requests.
The audit module of ARTURON grc connects audit programs, findings and corrective actions.
Audit program, audits, findings, and corrective and preventive actions. Responsible owners and evidence stay linked to the findings.
The business continuity module of ARTURON grc organizes the analysis of critical business processes and continuity planning.
Business processes with criticality, business impact analysis, emergency and recovery plans. Exercises and crisis team support continuity planning.
The Trust Center of ARTURON grc provides evidence selectively to chosen recipients.
Release evidence selectively per customer or auditor, without a user account for the recipient. Help articles, guided tours and learning paths support work in the system.
Your status in one view
Risks and fulfillment status in one shared overview. This shows where measures are missing and decisions are pending.
See the dashboard in a demo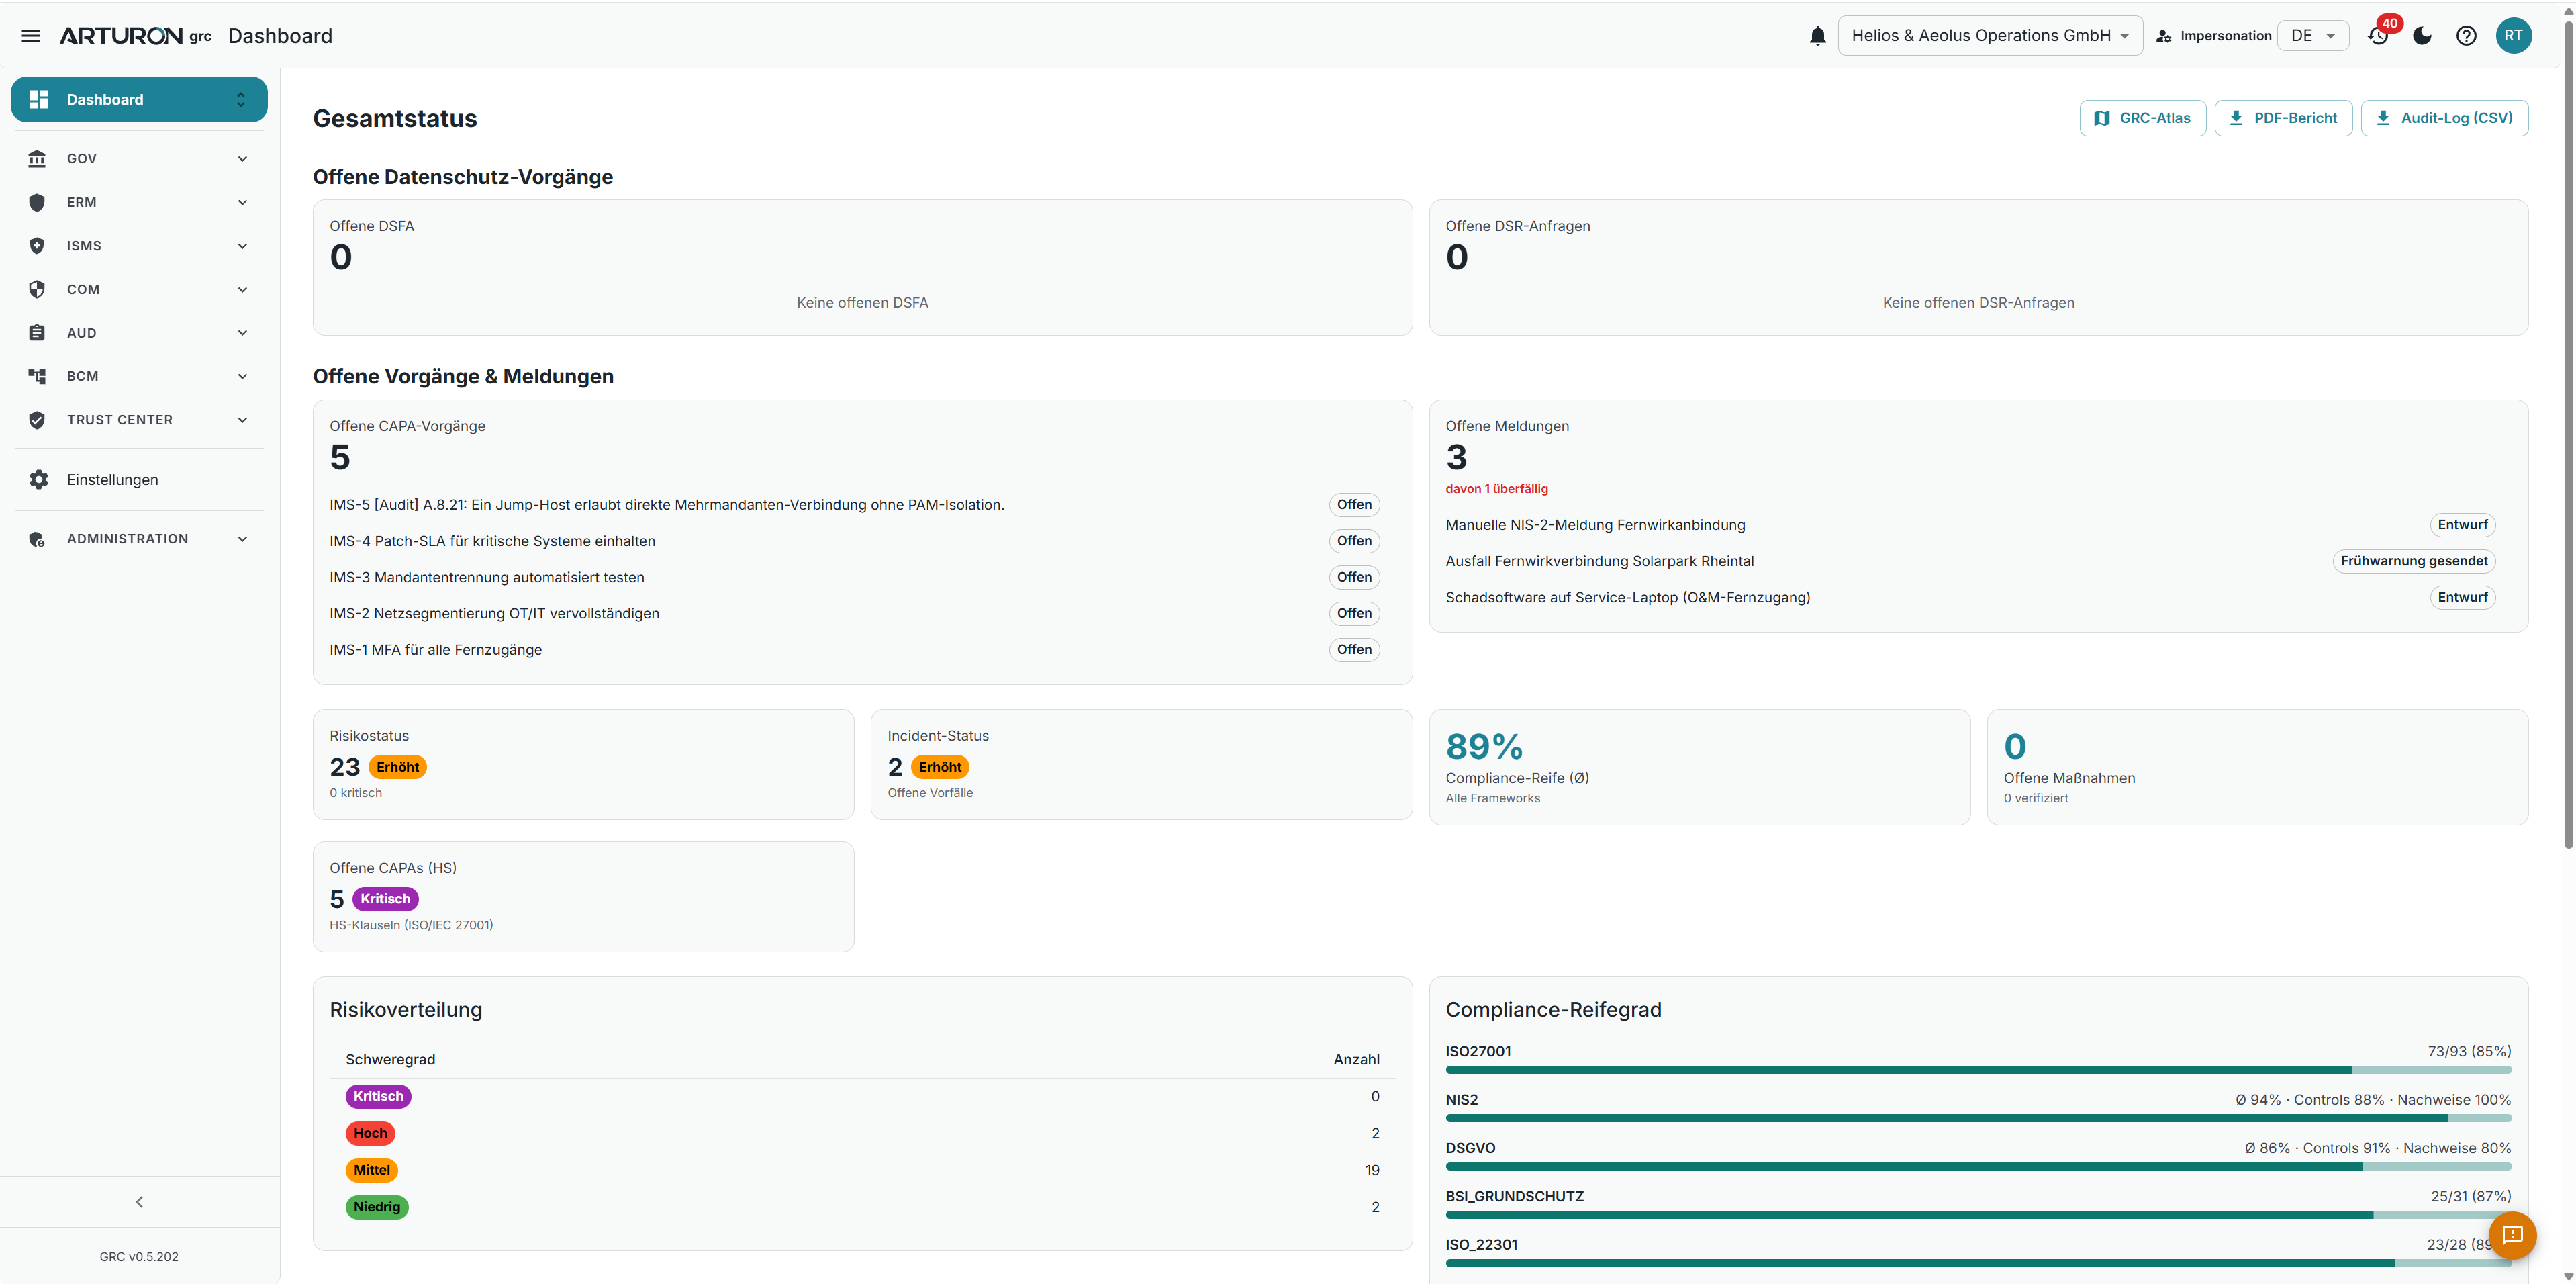
Frameworks in context
Requirements are assessed per company and translated into measures. The shared fulfillment matrix makes gaps visible.
Management system, risk management, statement of applicability and Annex A catalog as the foundation.
Assess applicability, organize incident reporting and bundle evidence including management decisions and training.
Assess requirements for energy companies separately. Manage the IT security catalog and ISO/IEC 27019 as frameworks, along with reports and certificate evidence.
Zones, conduits and security levels. Assign standard parts by role as operator, service provider, integrator or manufacturer.
Manage products with SBOM, vulnerabilities, conformity evidence and reporting.
Manage records of processing activities, data processing agreements, impact assessments, data subject requests and data protection incidents.
Connect business impact analysis, emergency plans, exercises and crisis team in continuity planning.
BSI IT-Grundschutz, TISAX and IEC 62351 in the fulfillment matrix. Security annexes and questionnaires from your clients as separate frameworks.
GRC-as-a-Service for O&M partners
Your operator customers pass requirements on to you through security annexes. With ARTURON grc, you extend your operations management with a GRC service.
One tenant per operator, one obligations register and evidence from maintenance and inspection. You build the management system once and reuse it as a basis for further customers. On request, RITTEC handles setup and operation.
Clarify applicable requirements and service scope per operator customer.
Set up customer tenants, assign assets and organize measures.
Deliver the agreed services, maintain evidence and report results.
Open to your systems
Assets from your own register or from connected systems. Vulnerabilities from DefectDojo and Dependency-Track. Evidence by link from existing documentation and ISMS tools.
Connectors for meteocontrol and Greengate and a REST API with OpenAPI description connect the platform to your system landscape.
To take away
The two-page GRC factsheet for O&M partners. Available in German and English.
Read the factsheet online · German →
Read the factsheet online · English →
We provide the detailed scope of services on request.
Request service descriptionARTURON grc organizes management and evidence. It does not monitor networks or detect attacks. The applicability assistant does not replace legal advice. Certification success is not guaranteed.
Questions and answers
ARTURON grc is software for governance, risk management, information security, compliance, audit and business continuity. It links requirements with responsible owners, measures and evidence.
ARTURON grc covers ISO/IEC 27001:2022, NIS-2 and BSIG, EnWG, IEC 62443, the Cyber Resilience Act, GDPR and business continuity requirements, among others. Contractual security requirements can be managed as separate frameworks.
A measure is maintained once and assigned to the requirements it covers. The related evidence stays linked to the measure. This creates one shared measure base for several frameworks.
O&M service providers manage operator customers in separate tenants, organize obligations and measures and release evidence selectively through the Trust Center. Services, responsibilities and releases are agreed per customer.
ARTURON grc organizes management and evidence. It does not monitor networks or detect attacks. The applicability assistant does not replace legal advice. Certification success is not guaranteed.
The next step
One-day preliminary analysis covering relevant frameworks, gaps and the right starting point, with a concrete proposal for your first three tenants.